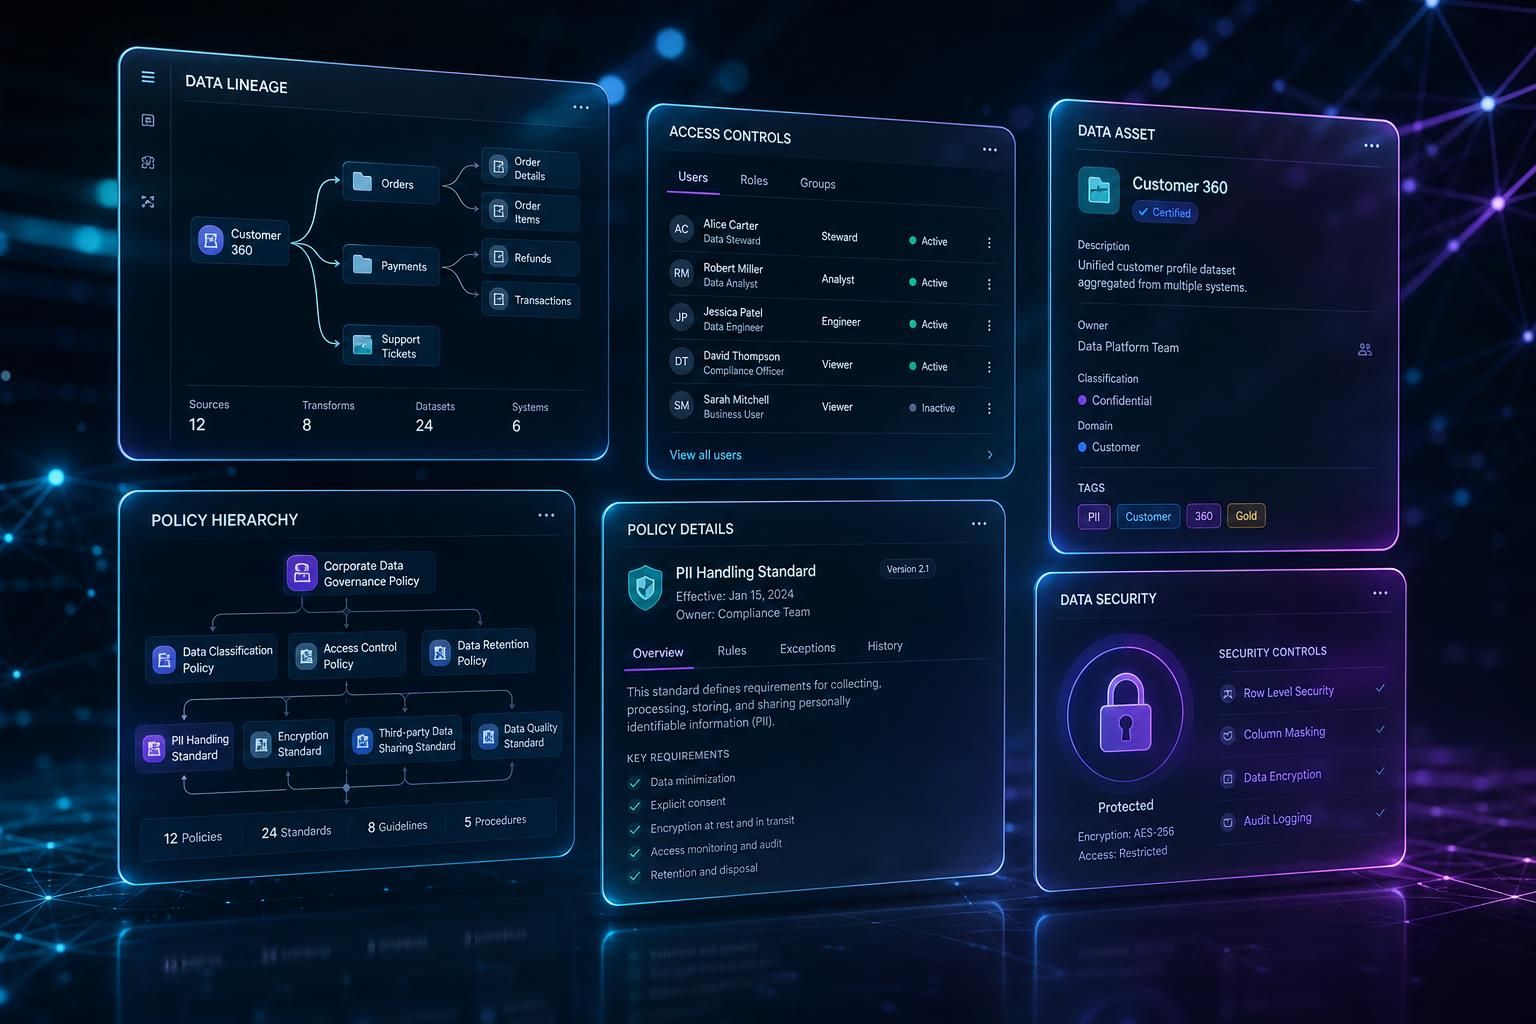
Data governance has a branding problem. To most healthcare leaders, it sounds like committees, policies, and steering meetings — overhead that slows things down. In practice, when governance is done well, it is the opposite: it is the operating system that lets analytics, AI, and reporting move faster with less risk.
At Brandywine Consulting Partners, we have helped healthcare organizations stand up governance programs that are practical, not bureaucratic. This article shares the framework we apply.
Start with the Decisions, Not the Data
Governance fails when it begins with cataloging every data element in the enterprise. By the time the catalog is "complete," it is already stale. We start instead with the decisions the organization needs to make — clinical quality, financial performance, operational throughput — and work backward to the data assets that support them.
This decisions-first approach produces a governance program scoped to what matters, with momentum from real outcomes rather than theoretical comprehensiveness.
Define a Few Clear Roles
Governance roles do not need to be complicated. We typically establish four:
- ▸Data owner — the business leader accountable for a domain (e.g., revenue cycle, clinical quality)
- ▸Data steward — the subject-matter expert who defines metrics and resolves data questions
- ▸Data custodian — the technical owner of the platform that stores and processes the data
- ▸Data consumer — anyone using the data to make a decision
Clear roles eliminate the "everyone is responsible, no one is accountable" pattern that kills governance programs.
Codify the Definitions
The single most valuable artifact in healthcare governance is a maintained business glossary — what counts as a "patient encounter," what an "active member" is, how "denied claims" are categorized. Without it, every analytics conversation re-litigates definitions.
We make the glossary live in the same tools the analytics team uses, version-controlled, and reviewed on a cadence. Definitions that drift get caught quickly.
Engineer Data Quality In, Don't Inspect It Out
Data quality is not something you achieve with a quarterly cleanup project. It is the cumulative result of upstream design choices: validation at point of capture, schema enforcement at ingestion, automated tests at every transformation, monitoring in production.
The practical pattern we apply on every engagement:
- ▸Source-system validations to prevent bad data at the source
- ▸Schema and contract enforcement at every pipeline boundary
- ▸Automated quality tests in CI/CD (uniqueness, referential integrity, range checks)
- ▸Production monitoring with alerts when quality metrics degrade
- ▸A clear escalation path when issues are detected
Treat Compliance as Built-In, Not Bolt-On
HIPAA, HITRUST, and emerging regulations like CMS interoperability rules are easier to satisfy when controls are baked into the data platform itself: encryption by default, centralized audit logging, attribute-based access control, automated PHI detection in new data assets.
Governance programs that try to satisfy compliance through procedure alone always lag the actual risk. The right answer is governance encoded in infrastructure, with procedure on top.
Make Access Granular and Auditable
In healthcare, fine-grained access control is mandatory, not optional. We help clients implement:
- ▸Row-level security so a user only sees the patients, members, or providers in their scope
- ▸Object-level security so sensitive columns (SSN, mental health flags) are visible only to authorized roles
- ▸Just-in-time elevation for break-glass scenarios
- ▸Comprehensive audit logs that satisfy both internal and regulator review
Measure the Health of Governance
If governance is working, it should be measurable: data quality scores trending up, time-to-onboard new data sources trending down, the number of conflicting metric definitions trending toward zero, audit findings closed within SLA. We help clients pick a small number of leading indicators and report on them publicly inside the organization, so the value of governance is visible.
Iterate, Don't Boil the Ocean
The most successful programs we have helped build started small — one domain, one critical use case, a 90-day window — and expanded based on demonstrated value. The least successful tried to launch enterprise-wide governance frameworks before they had earned the organizational trust to enforce them.
A Foundation, Not a Cage
Done right, governance is the foundation that lets healthcare organizations move fast on analytics, AI, and reporting with confidence. It is what makes "trustworthy data" a default rather than an aspiration. That is the outcome BCP partners with clients to achieve.
Ready to put this into practice?
BCP partners with healthcare and life sciences leaders to translate strategy into shipped, secure systems. Let's talk about your next initiative.
Talk to BCP